NIS2 · DIRECTIVE (EU) 2022/2555

NIS2: know in 48 hours what you must implement

NIS2 is the EU cybersecurity directive, applied through national laws in Czechia since 1 November 2025 and in Germany since 6 December 2025. A free assessment tells you whether and how it applies, with obligations and deadlines; implementation starts at €3,900 excl. VAT.

Quick and free:NIS2 applicability check

The obligations already apply. National laws in Germany and Czechia are in force and their registration deadlines have passed. Late registration is still better than none.

ReferencesT-Systems · Olingo Medical · Rowan Legal

Leave your number, I'll call you

Krystof Olik · founder and CEO

Same working day (CET), otherwise the next working morning.

Or email me directly at info@ollsoft.ai

We use your details only for this request. Privacy
Germany
in force 6 Dec 2025 (NIS2UmsuCG / BSIG)
Czechia
in force 1 Nov 2025 (Act No. 264/2025 Coll.)
Incident reporting
early warning within 24 hours (Art. 23 NIS2)
Fines
essential entities: a maximum of at least €10m or 2% of worldwide turnover, whichever is higher (Art. 34 NIS2)
PricingAssessment: freeImplementation: from €3,900Operation: from €390 per monthFull offer

Why Ollsoft?

We are engineers: we document the measures and set them up with your IT.

  • MFA, backups and logging set up with your IT, instead of a report it has to work through
  • AI drafts the documentation from your existing material and an engineer reviews every document; the AI runs in the EU or on your server
  • we build on ISO 27001 and your existing documents and add only what is missing
  • a fixed price in writing up front; deadline guarantee: documentation and measures plan within 90 days of receiving your input, or we keep working for free
  • we do the technical work and prepare processes and documentation; lawyers at our partner firm Rowan Legal validate them and prepare the contracts
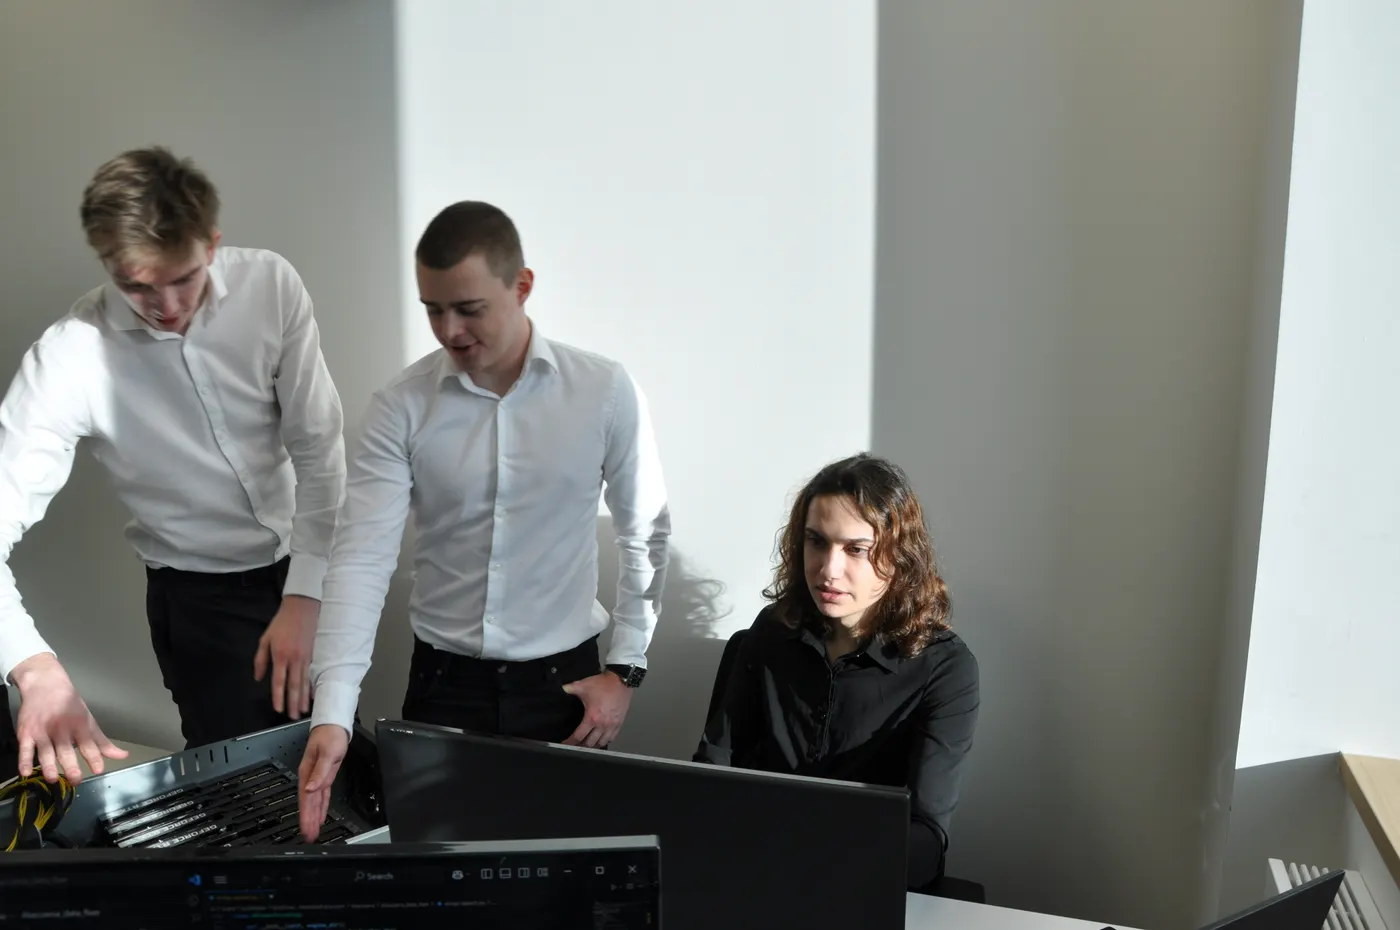
Ollsoft engineers at an open server and a workstation

Does NIS2 apply to my company?

NIS2 (Directive (EU) 2022/2555) is the EU cybersecurity directive; Germany implements it in the BSIG, Czechia in Act No. 264/2025 Coll. It applies to you if you operate in one of its 18 sectors and are at least a medium-sized enterprise, or provide a service covered regardless of size.

  • medium-sized: 50 or more employees, or more than €10m in both annual turnover and balance sheet total; partner and linked enterprises count
  • high-criticality sectors: energy, transport, banking, financial market infrastructure, health, drinking and waste water, digital infrastructure, ICT service management, public administration, space
  • other critical sectors: postal and courier services, waste management, chemicals, food, manufacturing (medical devices, electronics, machinery, vehicles), digital providers, research
  • regardless of size: DNS providers, TLD registries, trust services, public electronic communications networks
  • our NIS2 applicability check gives a quick first answer

What are essential and important entities?

Essential entities are generally large companies in the high-criticality sectors; important entities are the other covered medium and large companies.

  • large: 250 or more employees, or turnover above €50m and balance sheet total above €43m
  • obligations are similar, but essential entities face stricter supervision and higher fines
  • management must approve and oversee the measures and take part in training

What do I have to implement?

Cybersecurity risk management owned by management, and the ability to report incidents on time.

  • risk analysis and security policies approved by management
  • asset inventory, access control and multi-factor authentication
  • backups, recovery and business continuity
  • logging, detection and an incident reporting process
  • security requirements for suppliers
  • training for management and staff

OFFER

From a free assessment to NIS2 in operation

Step 1 · Start here

NIS2 initial assessment in 48 hours

You know whether and how NIS2 applies and what lies ahead.

Free

What you get

  • 30 minutes with an engineer, no access to your systems
  • entity class: essential or important
  • the obligations and deadlines that apply to you, including registration
  • a written summary within 48 hours
  • a quote with a fixed price to implement
Get the free initial assessment

Step 2

NIS2 implemented in 90 days

Documentation and measures plan finished within 90 days of receiving your input; we handle registration and set up the technical measures with your IT.

from €3,900excl. VAT, one-off

What you get

  • detailed review of your systems and infrastructure: gaps ranked by risk
  • registration with the national authority
  • risk analysis and security policies
  • MFA, backups and logging set up
  • incident reporting process (24 h)
  • training for management and staff
  • supplier clauses and questionnaires
Request a quote

Step 3

NIS2 in operation

Measures stay valid as your IT and the rules change.

from €390 per monthexcl. VAT

What you get

  • quarterly review
  • documentation updates
  • incident support
  • evidence for supervisors
Request a quote

GUARANTEE

90 days, or we keep working for free

If documentation and the measures plan are not finished 90 days after we receive your input, we keep working at no extra cost until they are. Technical setup also depends on your IT, so the deadline covers our part. The deadline guarantee applies to the "NIS2 implemented in 90 days" package.

Get the free initial assessment

Leave your number, I'll call you

Krystof Olik · founder and CEO

Same working day (CET), otherwise the next working morning.

Or email me directly at info@ollsoft.ai

We use your details only for this request. Privacy

PROCESS

How it works

  1. 01

    A short call

    Sector, size, services. No access to your systems.

  2. 02

    Assessment in 48 hours

    In writing: entity class, obligations, deadlines and a fixed price.

  3. 03

    Implementation in 90 days

    Systems review, documentation and technical measures, weekly status.

  4. 04

    Operation

    Quarterly review, updates, incident support.

REFERENCES

References and partners

T-Systems

Compliance platform for the Cyber Resilience Act: requirement mapping, repository checks, vulnerability monitoring.

Olingo Medical

More than 10 hospitals and clinics use our clinical documentation AI; in two university hospitals it runs entirely inside their network. Hospitals are regulated entities themselves.

Case study

Rowan Legal

Our partner law firm for the CRA and NIS2: it validates our work and prepares the contracts. We also built AI for the firm that runs on its own servers, with no external APIs.

rowan.legal

CONTACT

Start with a free initial assessment

We talk briefly about your company and services and send your entity class, obligations, deadlines and a quote for implementation in writing within 48 hours. Free, no commitment.

Leave your number, I'll call you

Krystof Olik · founder and CEO

Same working day (CET), otherwise the next working morning.

Or email me directly at info@ollsoft.ai

We use your details only for this request. Privacy

FAQ

What clients ask us

We build on your information security management system. During implementation we compare your existing measures with the national requirements and add only what is missing. Existing documentation is extended, not rewritten.

No. A call about your sector, size and services is enough. We review systems and infrastructure only in the paid implementation, with the access you give us.

The initial assessment is free. Implementation, including the detailed systems review, starts at €3,900 excl. VAT, depending on the number of services and the state of your IT. You get a fixed-price quote in writing with the assessment.

No. We are engineers who implement measures and documentation. Legal validation and contracts come from the lawyers of our partner firm Rowan Legal; we also work with your own auditor or lawyer.

Under Art. 23 NIS2: early warning within 24 hours of becoming aware of a significant incident, notification within 72 hours, final report within one month of the notification.